Skip to content
Live hacking

Hackers looking for vulnerabilities in your infrastructure, live

Define the scope, choose the hackers and watch live as they work on your infrastructure. You always know who is inside and what they are doing.

~200

Vulnerabilities found on average per event

34%

Of the findings are High or Critical severity

40+

Verified hackers taking part in each event

Live hacking gives you:

Real results

Real vulnerabilities identified, prioritised by severity (CVSS) and with remediation recommendations your team can implement right away.

Set up your event
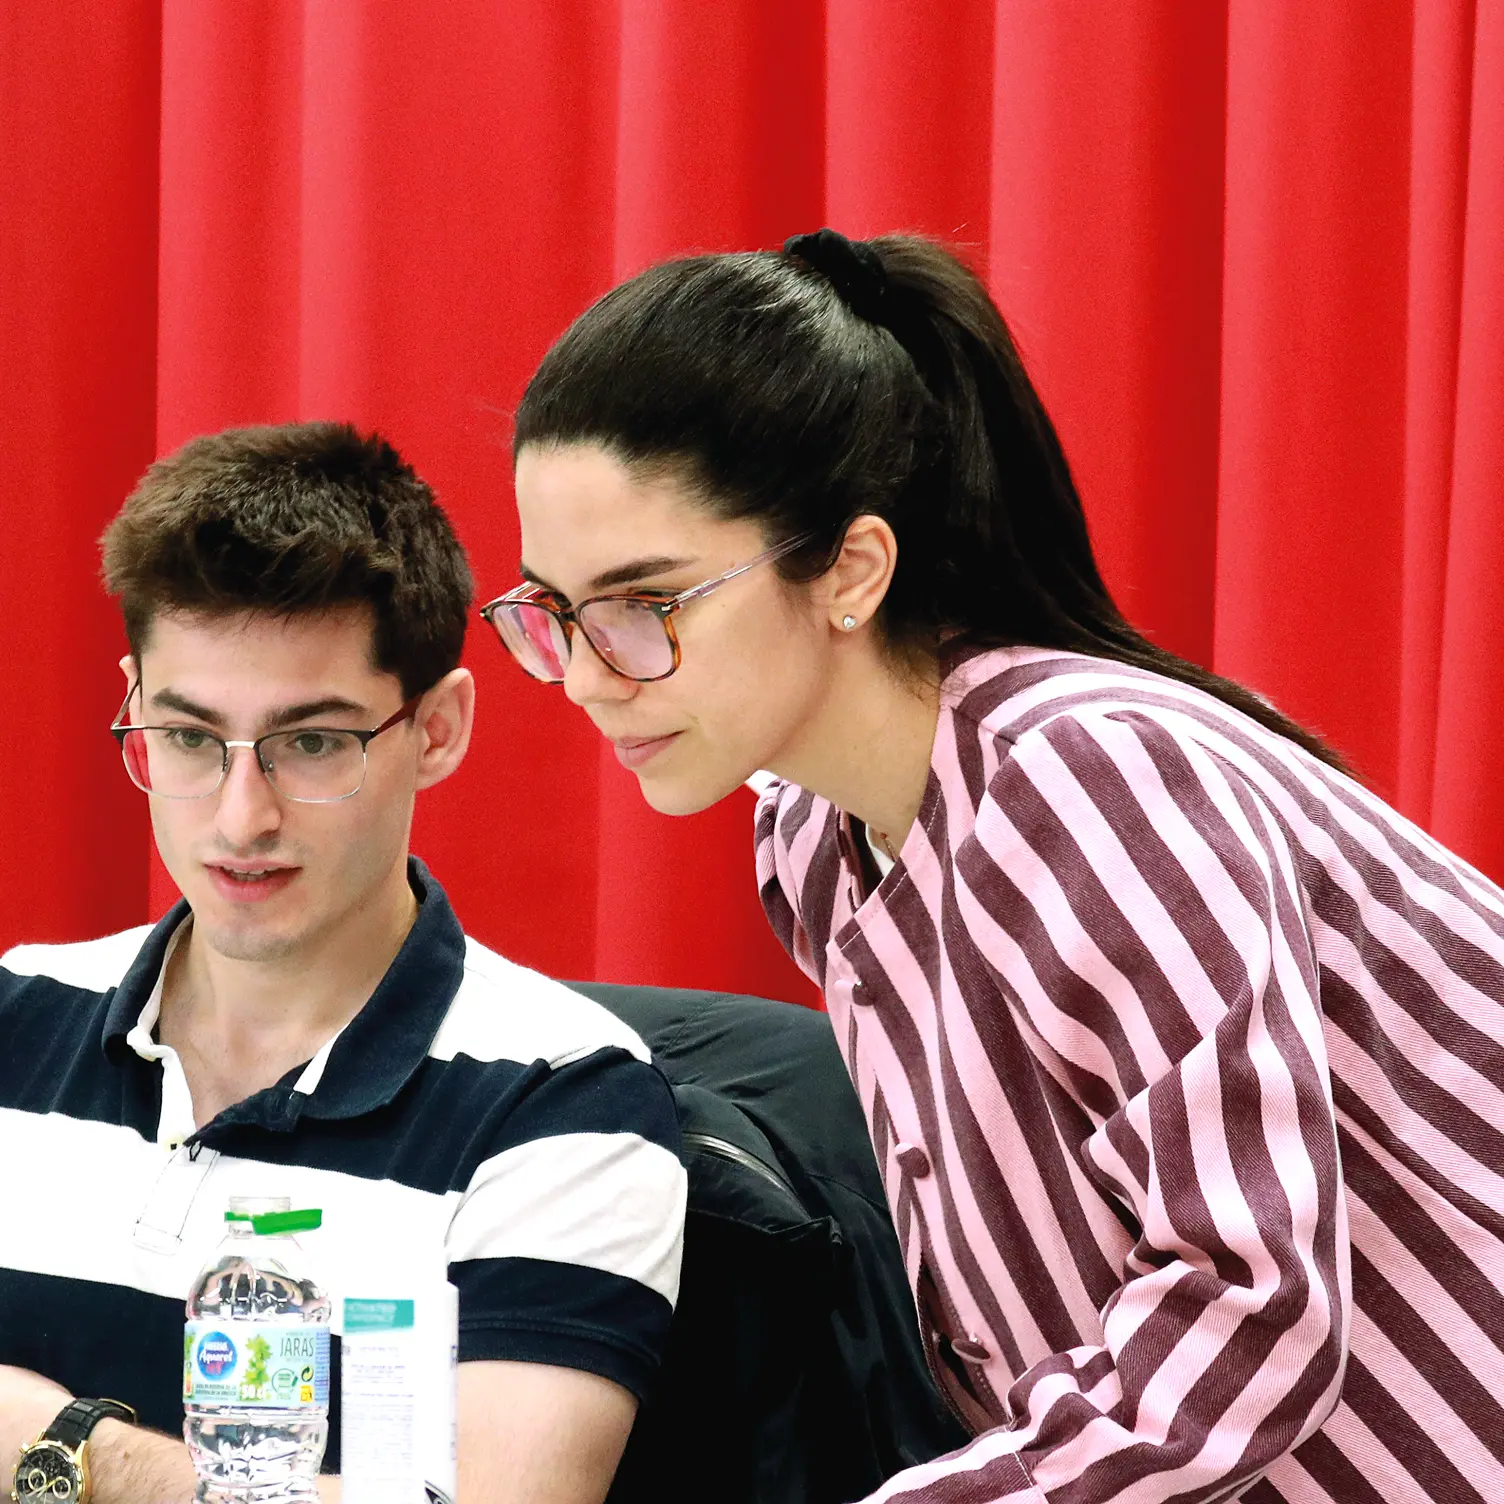
Full engagement

Your CISO, CTO and CEO watch the attack unfold in real time, in the same room or on a live shared screen.

Set up your event
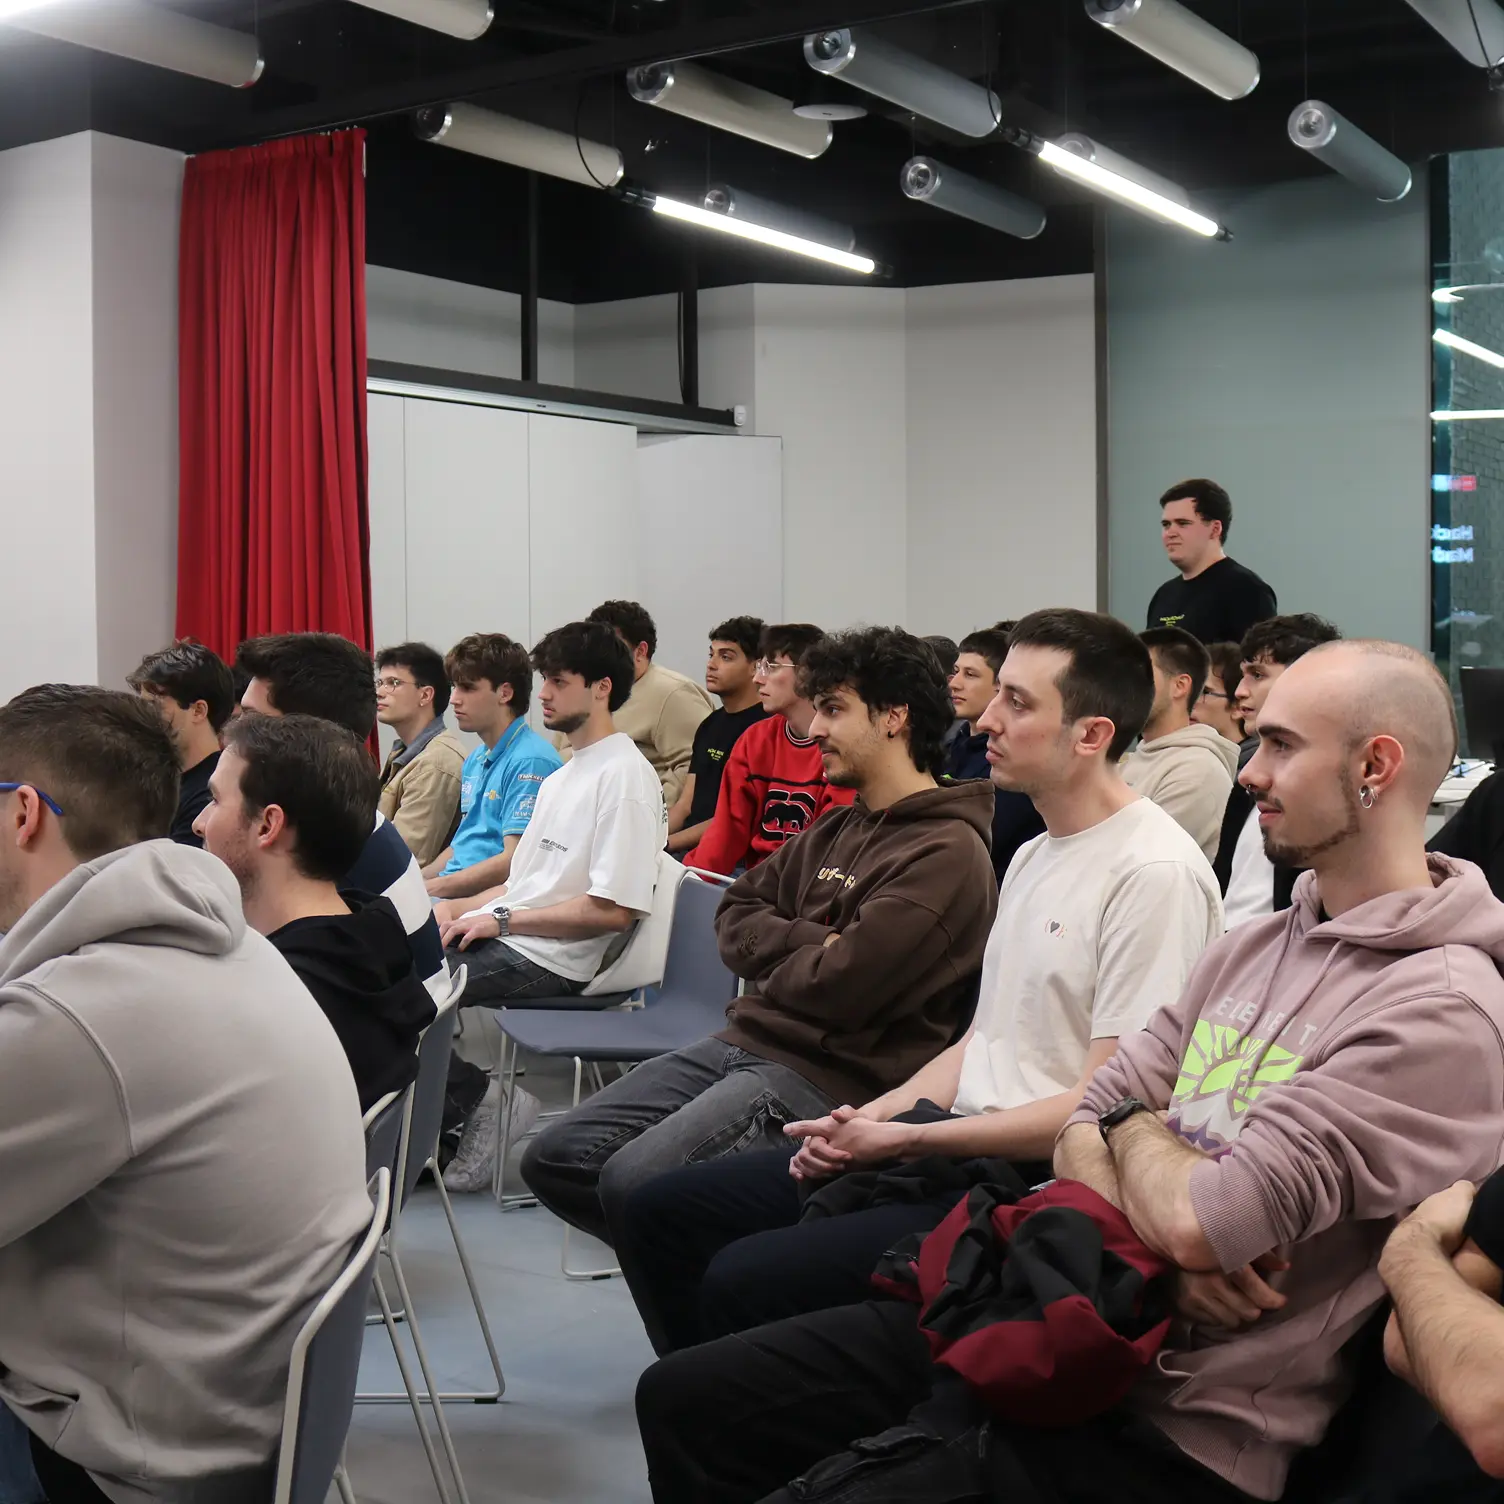
Clear ROI

Results in 2 to 3 days instead of the 3 to 6 months of a traditional audit, with the budget fixed from day one.

Set up your event
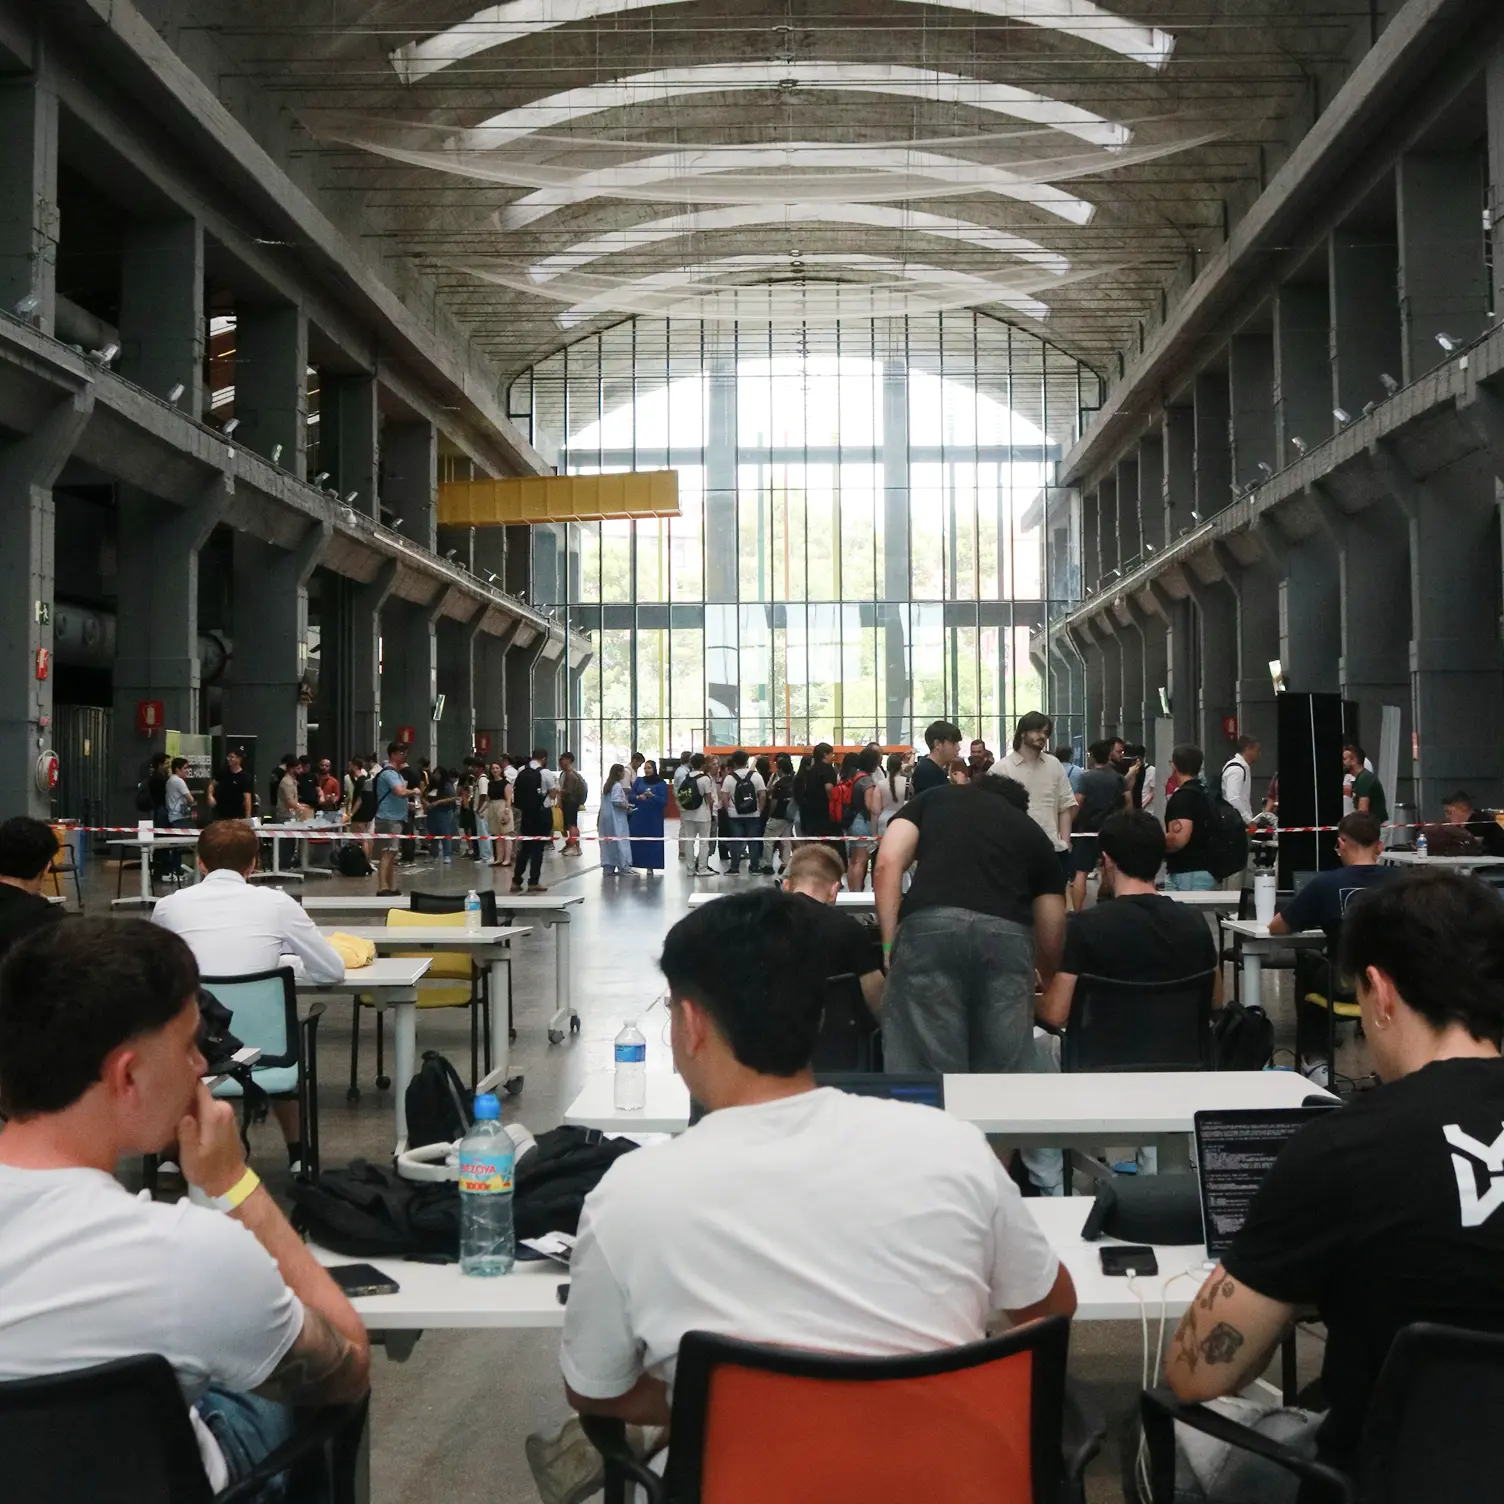
Make the event your own

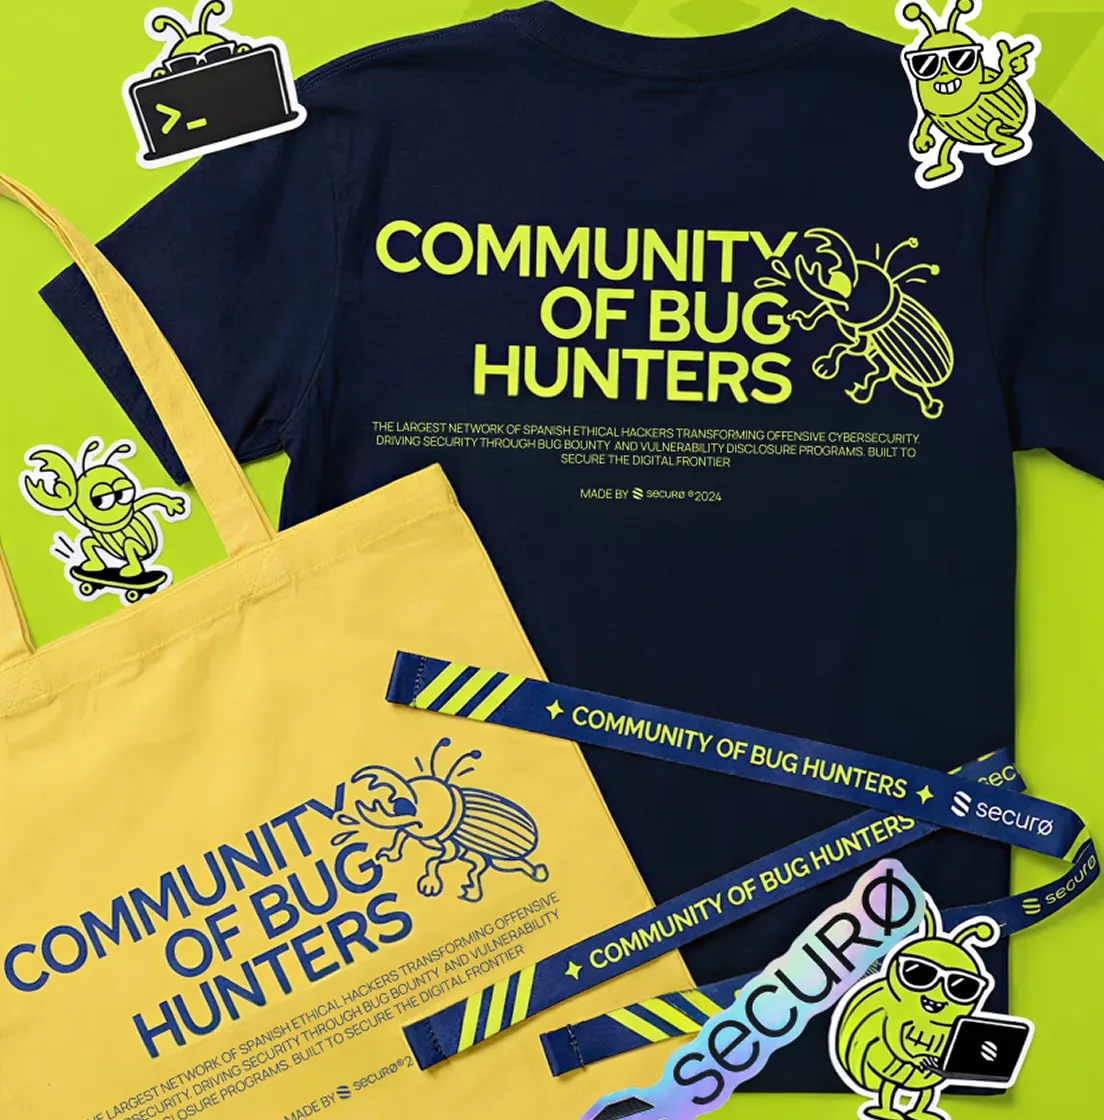
Make the event recognisably yours. We add branded merchandising, custom signage and whatever setting you need so the event feels part of your company, not a generic service.
Request information

How a live hacking event works

You set the scope and the budget

You choose which systems are attacked, what is out of bounds and whether the event is online, on-site or hybrid. You close the budget before starting, with no surprises.

You set the scope and the budget

We select the hackers, vetted one by one

We build a team around your sector and your systems. Every hacker is identified, verified and has a track record in previous events. No anonymous profiles.

We select the hackers, vetted one by one

You watch the attack happen in real time

Over 1 to 3 days, the hackers work under your supervision, on-site or with live shared screens. Every finding is validated on the spot.

You watch the attack happen in real time

You get a prioritised, actionable report

Vulnerabilities ranked by severity (CVSS), with technical evidence and a clear remediation plan. Results in days, not months.

You get a prioritised, actionable report

Frequently asked questions

Is it legal to open my systems to hackers at a live event?

Yes. Everything is governed by an ethical hacking contract that sets the scope, limits and authorisation in writing, in line with the GDPR and current legislation. The hackers only act within what you authorise.

How is it different from a bug bounty or a CTF?

Live hacking attacks your real infrastructure under direct supervision, within a fixed window of days. A bug bounty is continuous and has no on-site supervision; a CTF is an educational challenge in a neutral environment, not on your systems.

How do I control who gets into my systems?

Every hacker taking part is identified and verified in advance. You see who they are, what they do and when they do it, on-site or with live supervision if the event is online.

What if they try to exfiltrate data or go beyond the scope?

It is practically impossible without you seeing it: there is real-time supervision, the contract sets legal liability for any breach, and access is technically limited to what is authorised.

How much does a live hacking event cost?

It depends on the number of hackers, the duration and the scope. A small event (5 to 10 hackers, 1 day) starts at €8,000; a large one (40 to 50 hackers, several days) can exceed €50,000. We fix the budget before starting.

Can it be online, on-site or hybrid?

All three formats are possible. On-site gives the most impact and closeness; online lets hackers join from anywhere; hybrid combines remote hackers with your on-site team for a more realistic scenario.

We'll organise the best live cybersecurity event for you

Tell us the scope, the number of hackers and the format you're after, and we'll prepare a tailored proposal.