Skip to content
Crowdsourced Pentesting

Pentesting on demand: audit whenever you need to

Crowdsourced pentesting removes the waiting time of classic pentests. Launch audits on demand, get vulnerabilities as they are found and fix them without losing time.

More than 100 companies, of all sizes and sectors, already test their security with us

What is Crowdsourced Pentesting?
Continuous assessment of your security

Continuous assessment of your security

Continuous protection, without relying on a single snapshot once a year.
Analysis led by human experts

Analysis led by human experts

Qualified professionals who bring real judgement, beyond the scanner.
Vulnerabilities in real time

Vulnerabilities in real time

You hear about every finding the moment it happens, not weeks later.
Integrated with your development

Integrated with your development

It fits into your workflow and tests while you build (DevSecOps).
Go beyond compliance: ethical hacking that finds real vulnerabilities.

Exercises run by a team that thinks like a real attacker and that, along the way, leave you ready to meet the regulations your business needs.

Benefits of Crowdsourced Pentesting

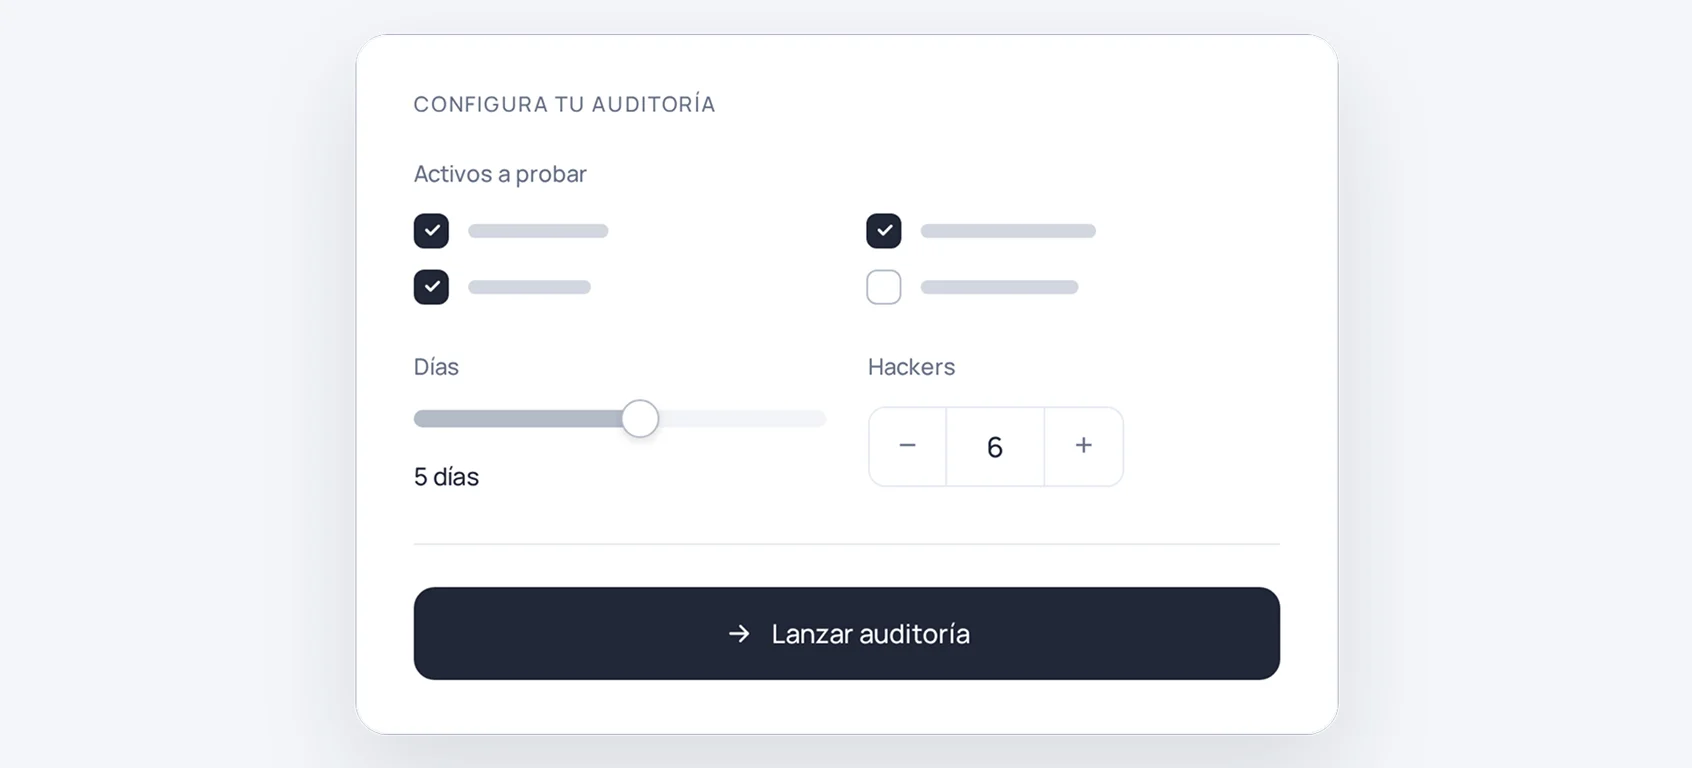
Design your test on demand, your way

Choose which assets to test, how many days and how many hackers, and launch your audit whenever you want. Fully tailored, with no closed packages.
Design your test on demand, your way

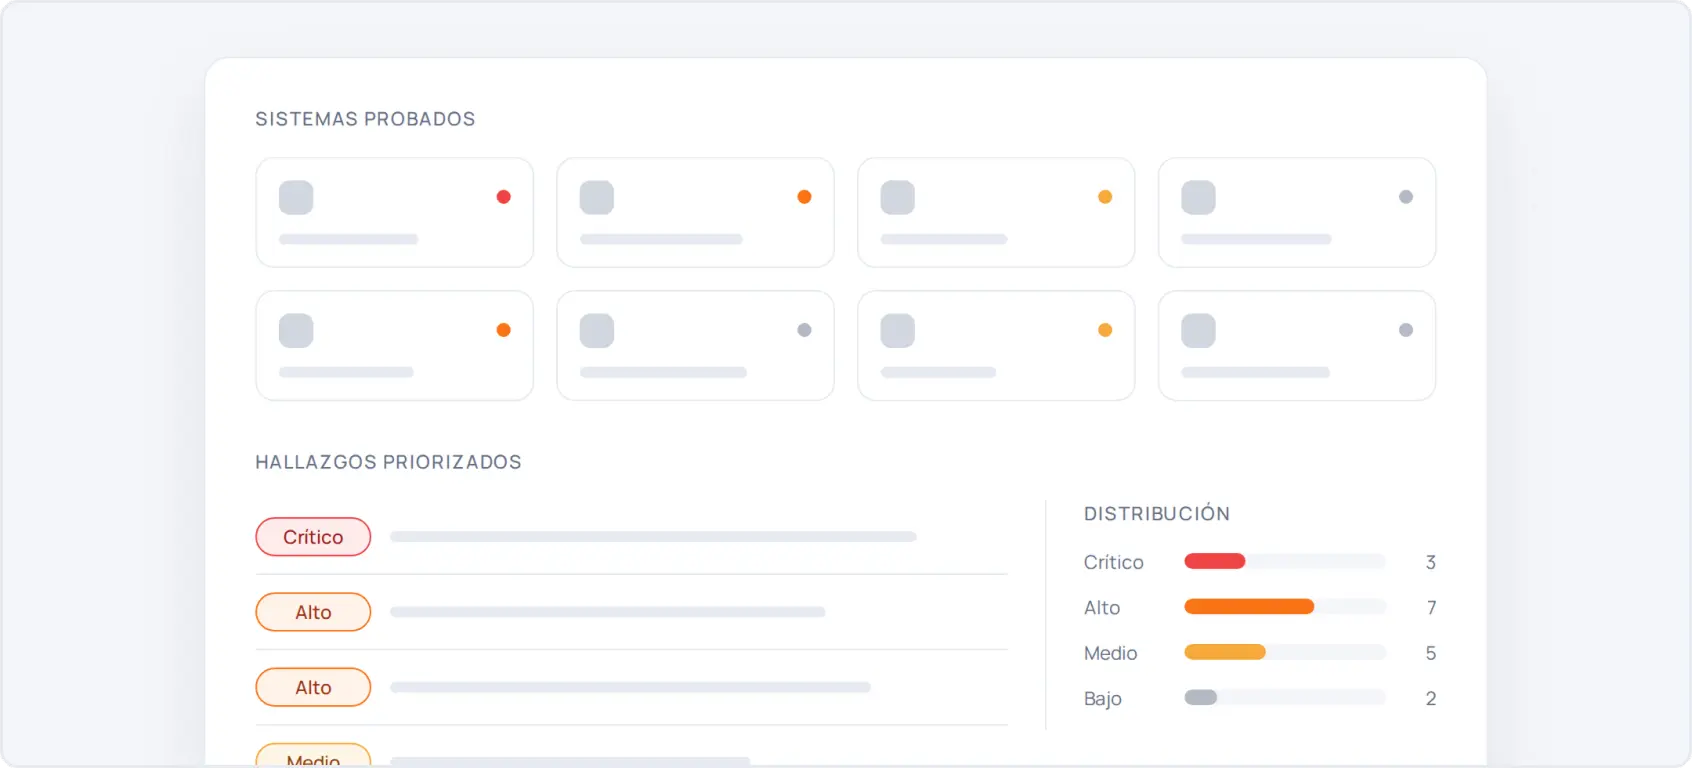
Real-time visibility

A single dashboard with everything found during the test, always up to date as the assessment of your systems moves forward.
Real-time visibility

Test during development (shifting security left)

Test while you build, before reaching production. You catch problems as they appear and avoid rebuilding in a rush at the end of development.
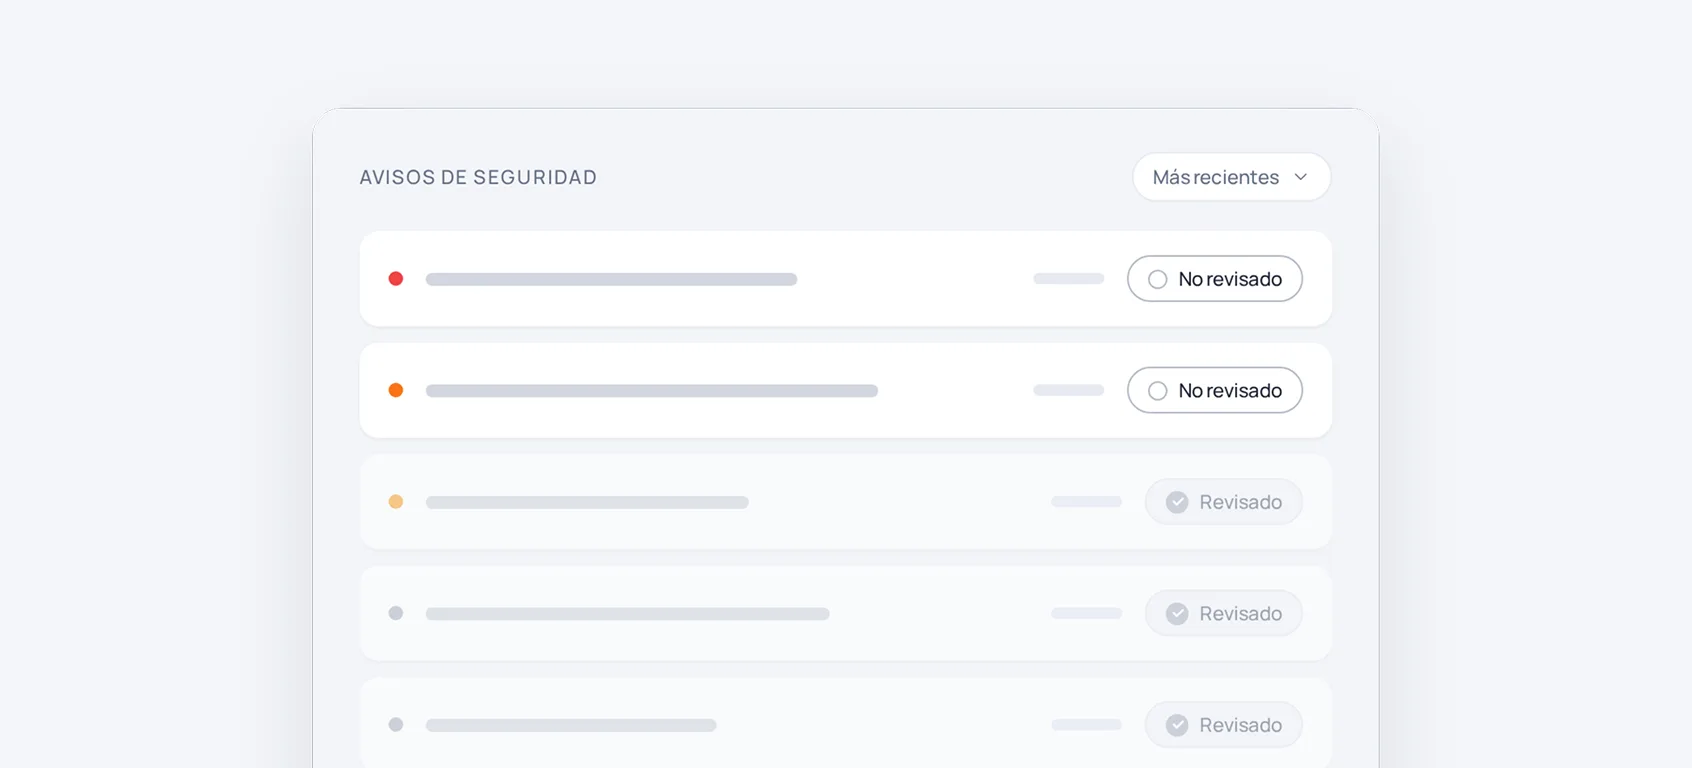
Test during development (shifting security left)

Expert manual testing + community

The value is in expert hands, beyond the automated scanner. Many providers over-rely on automation; we put real hackers to think about your system.
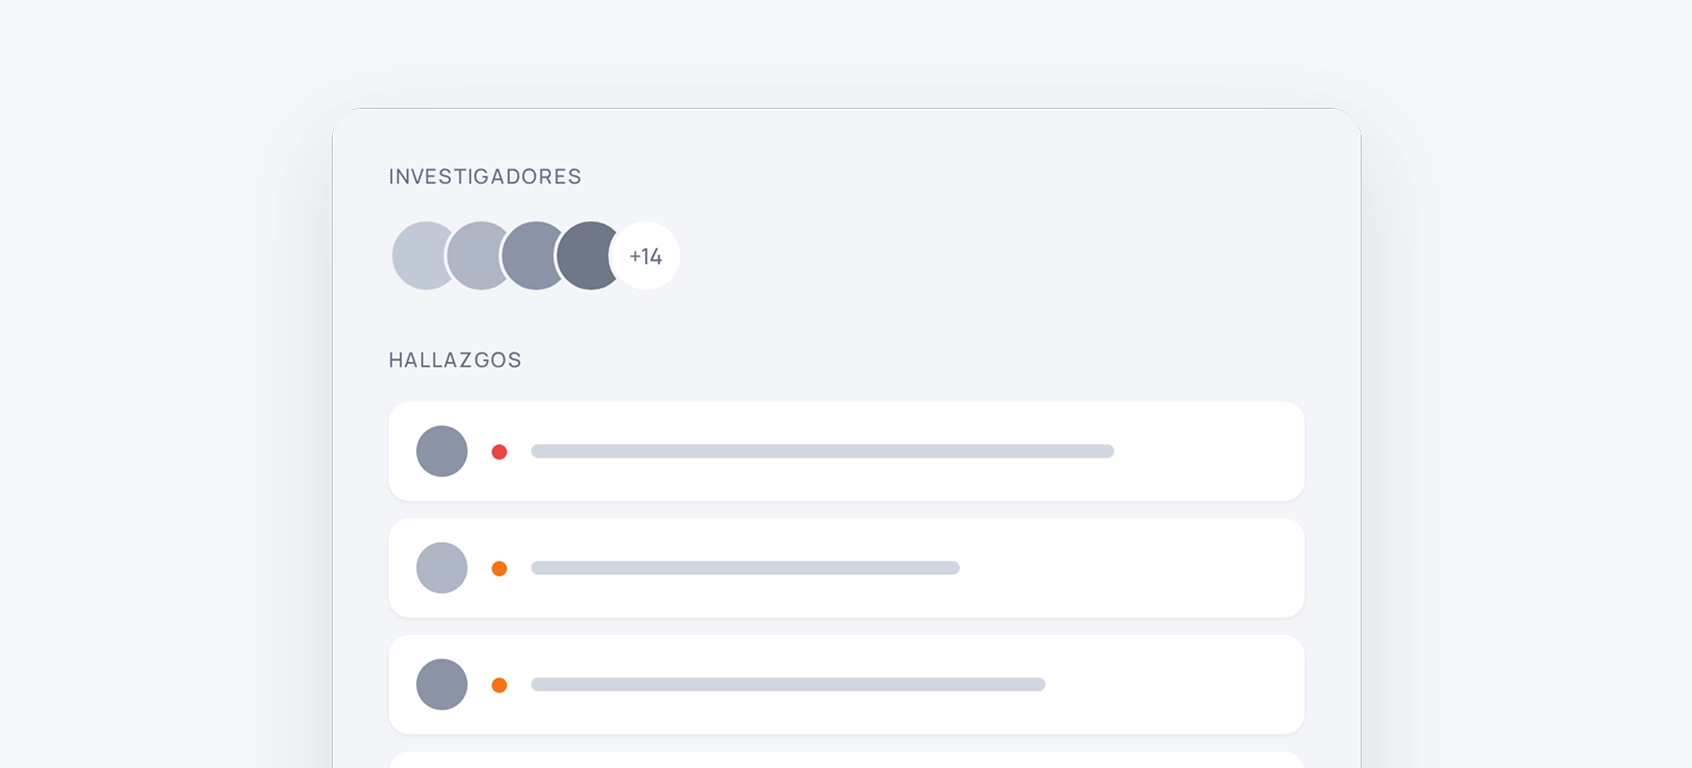
Expert manual testing + community

We re-validate your fixes at no extra cost

When you fix a vulnerability, we verify that it is properly resolved with as many re-assessments as you need. No expensive consultants every time, no surprises on the invoice.
Certified ethical hackers at your disposal
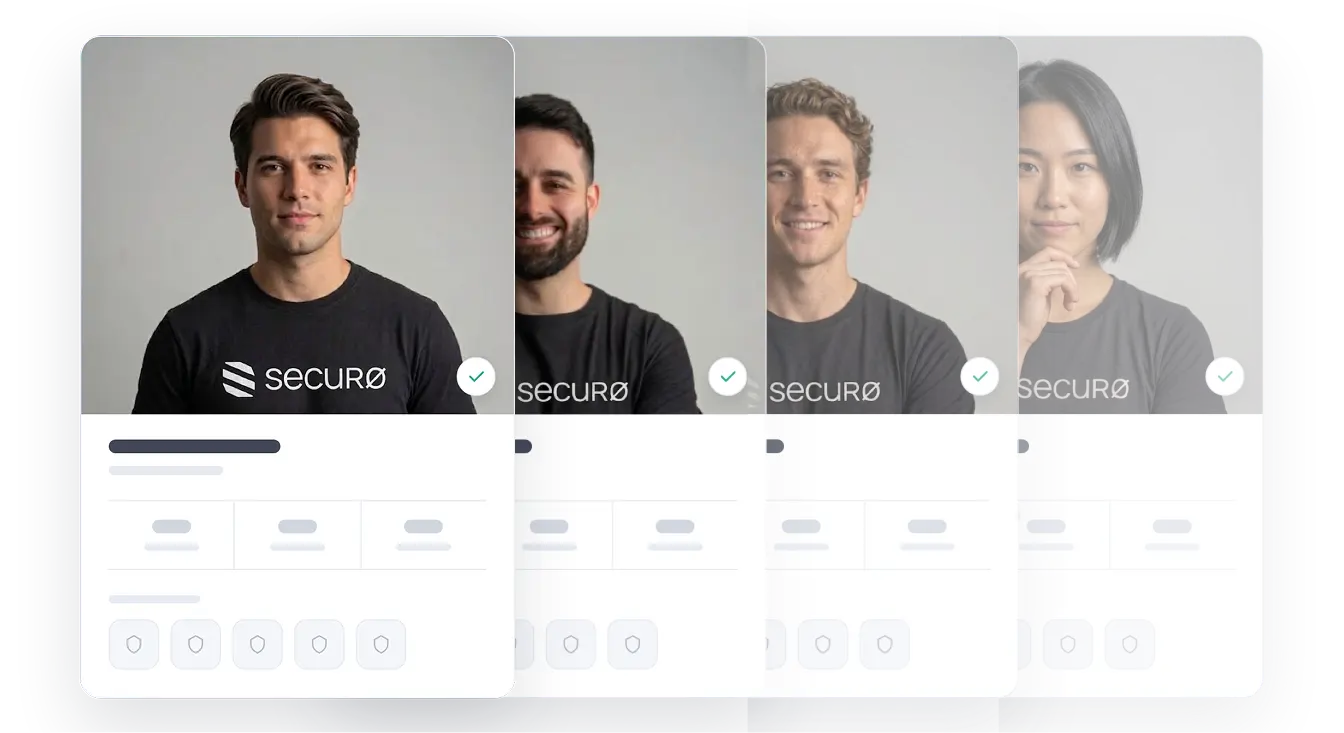
Certified ethical hackers at your disposal

We audit your entire perimeter

Web API AI agents / LLM Mobile (Android and iOS) Active Directory Desktop applications Cloud infrastructure Containers / Kubernetes WiFi Networks IoT / OT Source code (white box) Web3 Red Team

Frequently asked questions

What is crowdsourced pentesting?

It is a continuous pentesting model in which a community of expert hackers tests your systems on demand, instead of a single one-off exercise once a year. It combines the depth of a traditional pentest with the coverage and speed of many researchers working at the same time.

How is it different from a traditional pentest?

A traditional pentest is a one-off exercise run by a small team at a specific moment. Crowdsourced pentesting is continuous, many hackers run it at the same time and you get the findings in real time, with retests included to verify your fixes.

How is it different from a bug bounty?

Crowdsourced pentesting has a defined scope and methodology, with a formal report valid for compliance. A bug bounty is an open, permanent programme that pays for each vulnerability found. Many companies start with crowdsourced pentesting and add a bug bounty later.

Do retests cost extra?

No. We re-validate your fixes as many times as you need at no extra cost, so you can confirm that every vulnerability is properly resolved.

Does it help me meet regulations?

Yes. Every exercise is delivered with a formal report valid for certifications such as ISO 27001, ENS or PCI DSS, just like a traditional pentest, but with the advantage of being continuous.

Test your security whenever you need to, not once a year

Tell us about your case and we will put together a continuous pentesting programme tailored to your systems and regulations.