Pentesting that goes a step beyond the checklist
Ethical hacking exercises run by a team that thinks like a real attacker — not just to find vulnerabilities, but to help you meet the regulations your business needs.
More than 100 companies, of all sizes and sectors, already test their security with us


The pentest you need for any regulation.
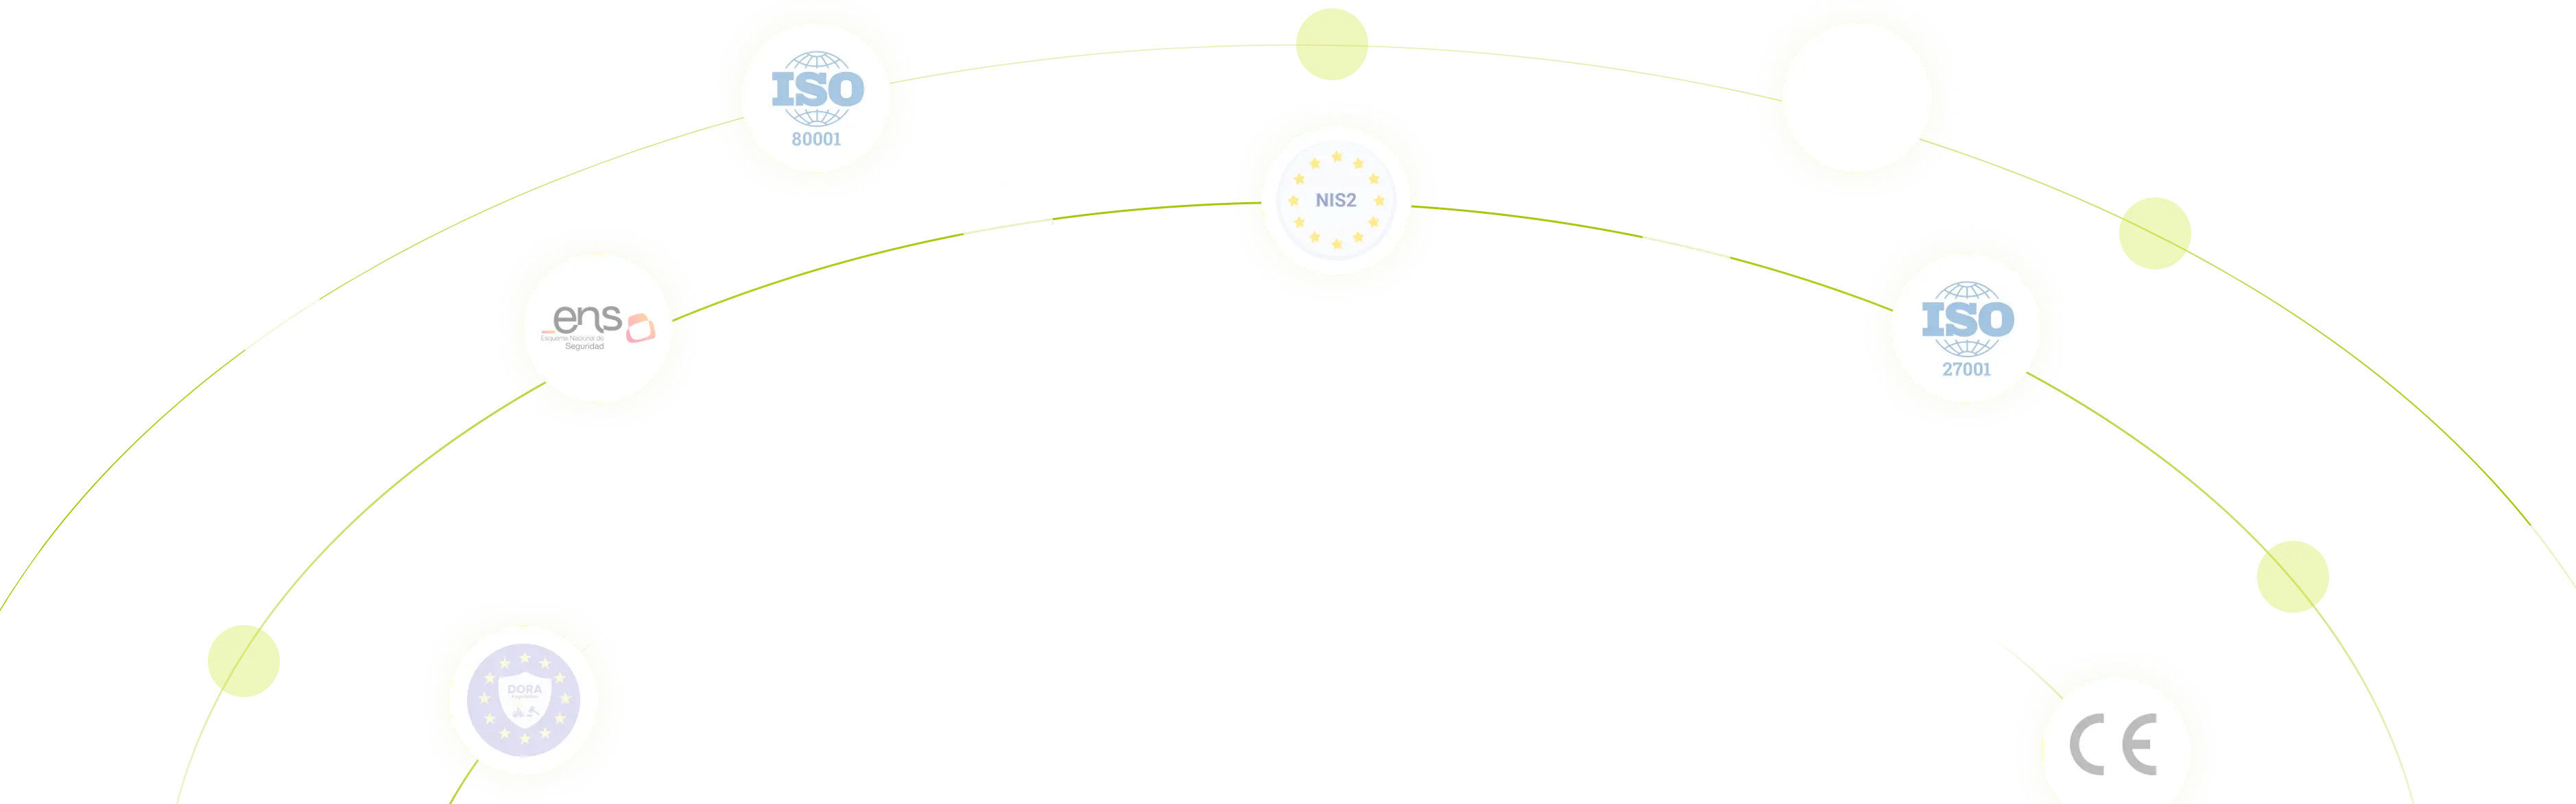
We have already helped our clients achieve ISO 27001, ENS, PCI DSS, FDA and many others. Tell us which one you need and we will help you get it.
Pentesting run by a team officially recognised in vulnerabilities.
We are one of the few CVE Numbering Authority (CNA) organisations authorised in Spain. Our team does not just find vulnerabilities: it coordinates the whole process of responsible management and disclosure, recognised by INCIBE and MITRE.
A pentest that does not stop at the report
Real visibility of your security
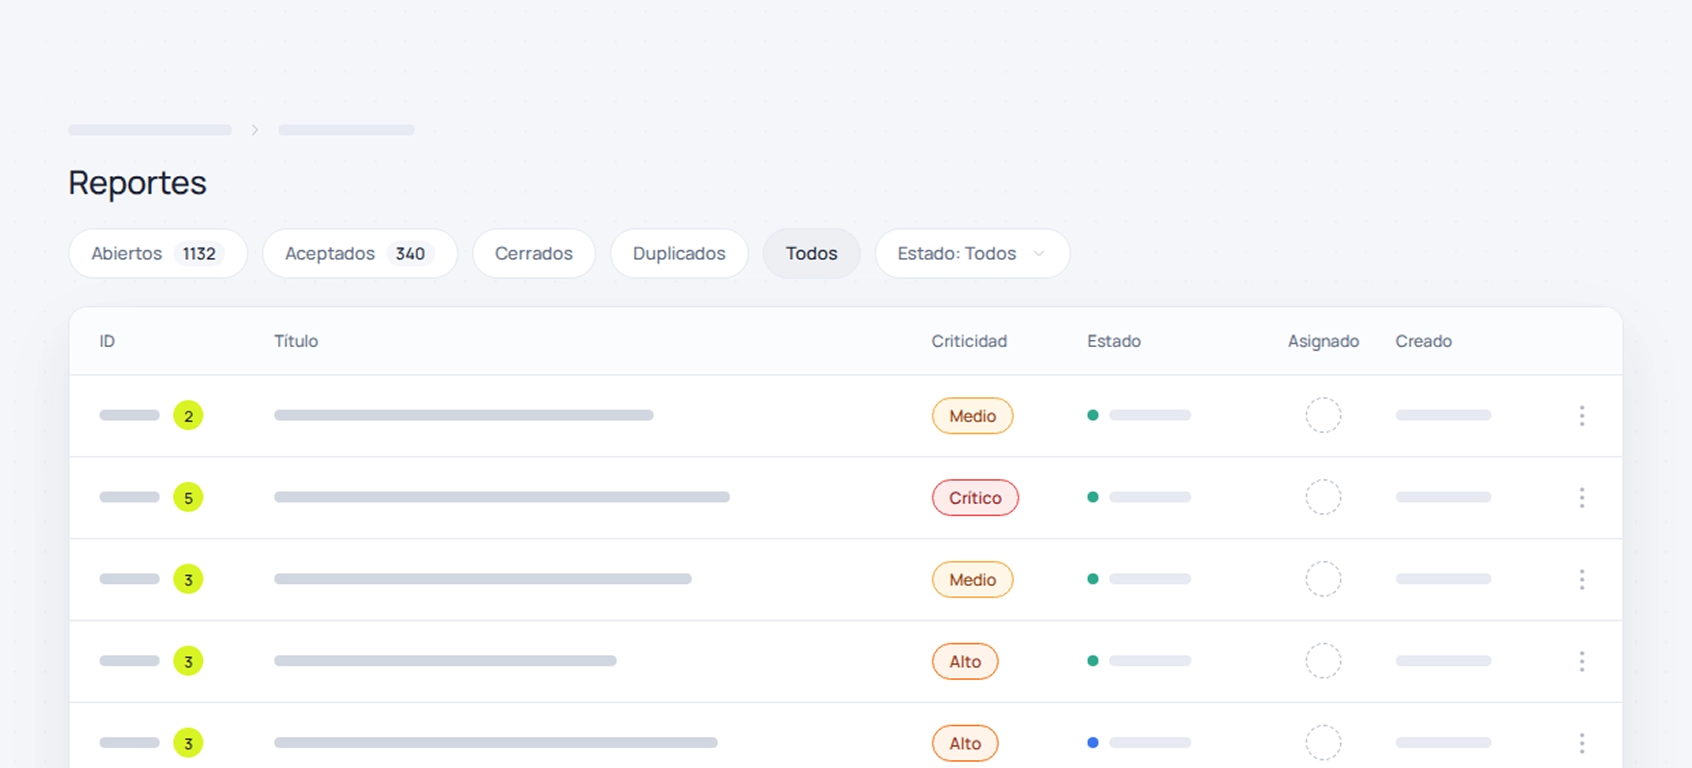
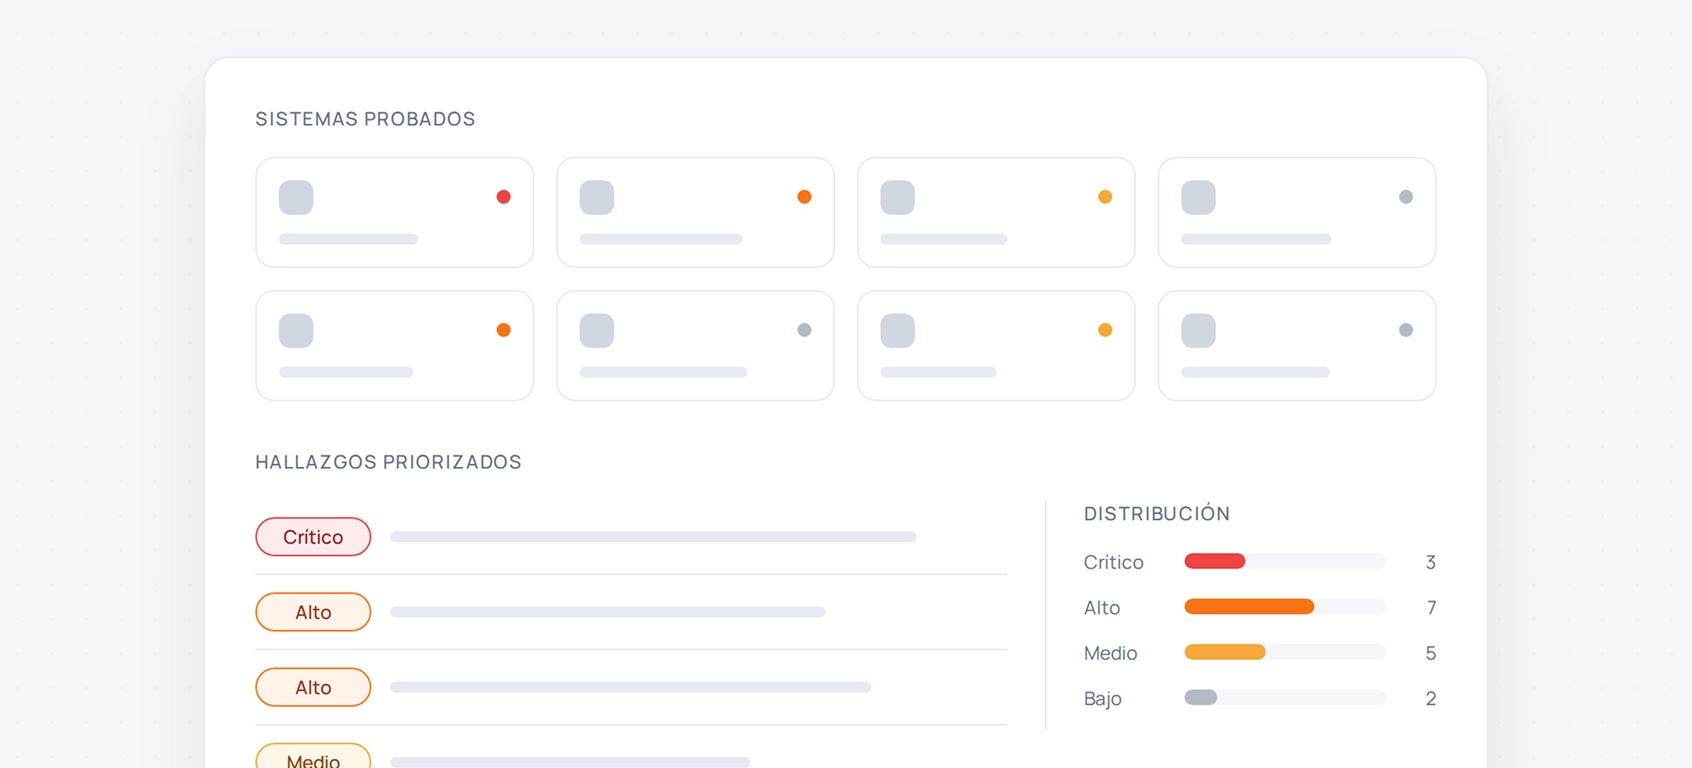
We test your systems the way an attacker would and give you a clear, prioritised picture of where you are exposed.
Test your systems and secure compliance
Every finding arrives documented and traceable, ready to present to auditors and clients. The pentest you need to certify, built for you to pass.
Fix fast and verify
We prioritise by criticality and verify the fixes with a retest, so you actually close the loop instead of being left with just a PDF.